
September 2026 recorded 862 publicly disclosed ransomware victims, 26.3% down from August’s 1,170. This is the final September figure in CYFIRMA’s leak-site tracker, captured after full-month collection. Thegentlemen (105) led monthly activity, followed by Qilin (74), Akira (36) and Storm (36). Organizations within Professional Goods & Services, Healthcare, Manufacturing, Real Estate & Construction, Consumer Goods & Services and Information Technology experienced the highest levels of targeting. Data theft, edge/VPN and RMM abuse, identity compromise, and multi-layered extortion continued to shape outcomes. Organizations should strengthen identity security, edge-device hardening, accelerated remediation, visibility, and proactive threat intelligence.
Confidence levels (High / Moderate / Low) used in this report reflect the volume and independence of the source reporting behind each assessment.
Who should read this: organizations in professional services, healthcare, real estate and construction, consumer goods, manufacturing and IT services, particularly in the United States, India, Canada and the United Kingdom, and any organization running internet-exposed Fortinet SSL-VPN, N-able N-central or other RMM consoles, commercial RMM agents (MeshAgent, Atera, ScreenConnect, Splashtop, NinjaRMM, SimpleHelp), Windows endpoints without vulnerable-driver blocking, or Azure tenants with broadly privileged service principals. Each of these technologies appears in September intrusion reporting as an access, control, or impact vector.
This edition of RANSOM WATCH covers ransomware activity observed in September 2026. It delivers a detailed analysis of the ransomware landscape, highlighting the emergence of new ransomware groups, evolving attack techniques, and notable shifts in targeted industries. By examining key trends, tactics, and significant incidents, this report aims to support organizations and security teams in understanding the current threat environment.
MOST ACTIVE RANSOMWARE GROUPS: TOP 10 TREND COMPARISON
Throughout September 2026, there was notable activity from several ransomware groups.
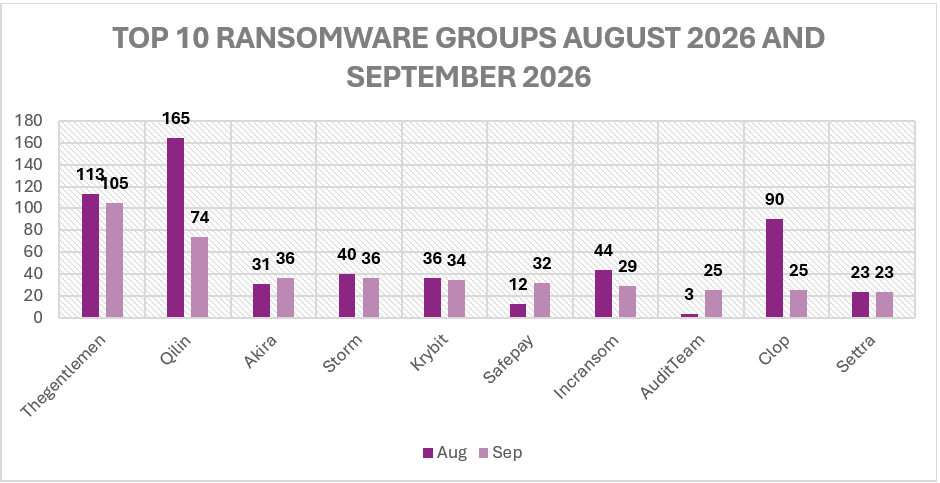
The August–September 2026 data indicates continued redistribution of ransomware activity. Leading operators included Thegentlemen (113 → 105), Qilin (165 → 74), Akira (31 → 36), Storm (40 → 36), Krybit (36 → 34), Safepay (12 → 32), Incransom (44 → 29), AuditTeam (3 → 25), Cl0p (90 → 25), and Settra (23 → 23). Safepay and AuditTeam were the strongest risers inside the top ten; Qilin and Cl0p posted the steepest declines among high-volume August brands. Overall, the RaaS ecosystem remains highly resilient, with operational capacity shifting among leaders and newcomers rather than signaling a collapse in overall ransomware threat.
NEW ENTRANTS AND EXITS
Compared with August, CYFIRMA’s tracker recorded 13 ransomware brands with September leak-site activity that had no August activity, led by Vexy Ransomware (19), N0n (18), Lamashtu (10), EndZone (5), Spirals (4), BlackLocks (3), Fulcrumsec (2) and Netrunner (2). Conversely, 21 August-active brands posted no September victims in the tracker, including L Group (28 in August), Coinbasecartel (24 in August), Helix (8 in August), Xpl0itrs (7 in August), Deadlock (6 in August), AiLock (4 in August), Nasirsecurity (4 in August), and Lynx (3 in August). Brand churn of this kind is expected in a RaaS marketplace and should be read as redistribution of disclosure capacity, not disappearance of shared access and extortion tradecraft.
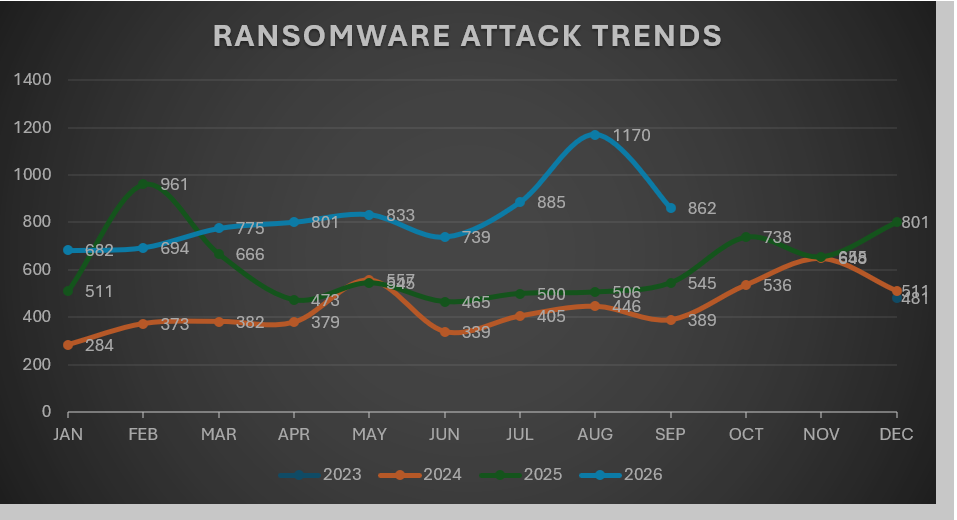
RANSOMWARE ATTACK VOLUME: MONTHLY TREND
Publicly disclosed incidents totaled 862 in September, compared with 1,170 in August (26.3% down month-on-month). Multi-year volumes continue to show that RaaS operations remain active and adaptable across industries and regions, even when monthly disclosure totals fall back from an exceptional prior-month peak.
VICTIM TRENDS BY INDUSTRY
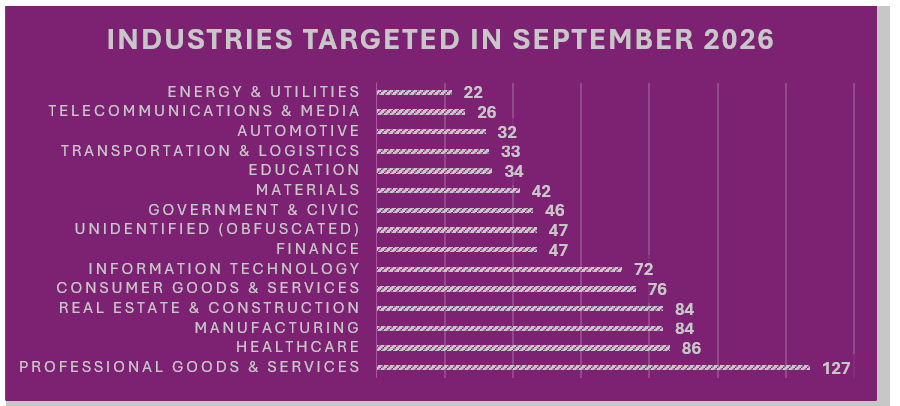
In September 2026, ransomware activity continued to focus on sectors where operational disruption and data theft maximize extortion. Month-on-month industry counts versus August included Professional Goods & Services (194 → 127), Healthcare (123 → 86), Manufacturing (169 → 84), Real Estate & Construction (128 → 84), Consumer Goods & Services (91 → 76), Information Technology (112 → 72), Finance (62 → 47), Government & Civic (56 → 46), Materials (33 → 42) and Education (29 → 34). Professional Goods & Services remained the most targeted vertical even as overall volume fell back from August’s peak, while Healthcare overtook Manufacturing for second place.
Operators continue to prioritize industries where business disruption and sensitive information exposure increase the likelihood of successful extortion.
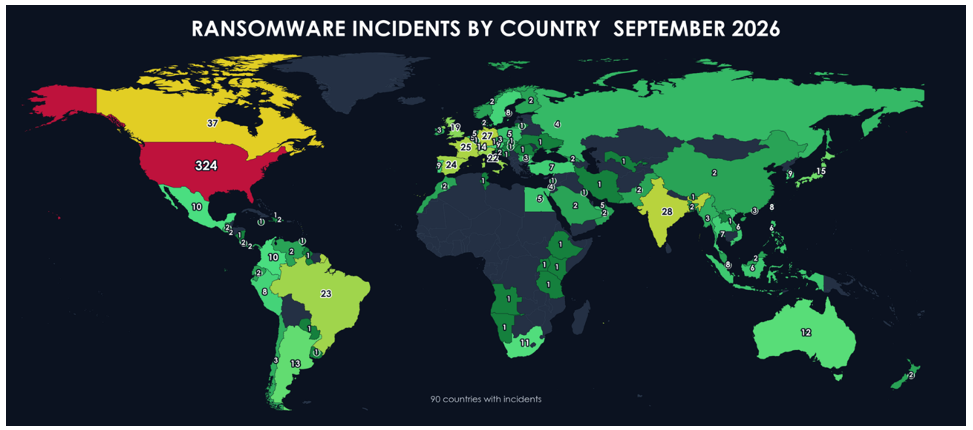
Ransomware activity in September 2026 remained geographically concentrated in the United States, which recorded 324 publicly disclosed incidents (38% of the total). Month-on-month country counts versus August included the United States (478 → 324), Canada (42 → 37), India (29 → 28), Germany (54 → 27), France (30 → 25), Spain (20 → 24), and Brazil (23 → 23). In total, 90 identified countries were affected. Operators continue to prioritize digitally mature economies while maintaining a broad international footprint.
VICTIM TRENDS BY ORGANIZATION SIZE
CYFIRMA’s leak-site tracker does not currently record victim organization size, so no breakdown by employee or revenue band can be given for September 2026. Enrichment of the tracker to support this view is being assessed for future editions of RANSOM WATCH.
DATA-LEAK-SITE ACTIVITY
CYFIRMA’s September 2026 leak-site and underground monitoring captured 862 victim postings across tracked data-leak sites, against 1,170 in August. Thegentlemen led disclosure tempo with 105 posts, followed by Qilin (74), Akira (36), and Storm (36). Newly observed or returning leak-site brands included Vexy Ransomware (19), N0n (18), Lamashtu (10), EndZone (5), Spirals (4), and BlackLocks (3). Posting patterns remained batch-oriented: multi-victim dumps from mature RaaS brands ran in parallel with concentrated debut campaigns from newer extortion brands seeking marketplace visibility.
EVOLUTIONS IN THE RANSOMWARE THREAT LANDSCAPE, SEPTEMBER 2026
Cross-RaaS Affiliate Tradecraft Stabilizing Faster Than Ransomware Brand Identity
This activity demonstrates the evolution of ransomware operations toward affiliate-centric consistency that outlasts any single encryptor brand. Microsoft Threat Intelligence reporting published in late September 2026 showed Storm-2570 maintaining largely uniform remote-access, discovery, credential-theft, Defender tampering, and cloud-exfiltration tooling across deployments involving Qilin, DragonForce, Anubis, and BERT. The technical signal is that payload family labels increasingly obscure the durable intrusion behaviors defenders can interrupt, while affiliates treat RaaS brands as interchangeable monetization endpoints rather than distinct technical stacks.
ETLM Assessment:
Ransomware risk programs are expected to keep shifting from brand-first tracking toward affiliate and tooling fingerprinting, because shared post-compromise playbooks will continue spanning multiple encryptor ecosystems (High confidence). Detection engineering that keys only on final ransomware binaries will miss the longer pre-encryption window where MeshAgent, PsExec, ntdsutil, and cloud sync utilities already establish impact conditions. Organizations should prioritize behavioral hunting for recurring affiliate toolchains irrespective of which RaaS name appears on the ransom note.
Commercial RMM Suites Becoming the Default Hands-on-Keyboard Control Plane for Affiliates
This development highlights the maturation of ransomware post-compromise control around legitimate remote monitoring and management platforms rather than custom command-and-control (C2) alone. September 2026 analyses of Storm-2570 and Settra-linked activity repeatedly documented MeshAgent, Atera, ScreenConnect, Splashtop, Remotely_Agent, and NinjaRMM as operational bridges for command execution, account manipulation, and lateral expansion. Actors further tailored MeshAgent deployments with victim-themed binary and service names and Base64-obfuscated command channels, converting enterprise-trusted RMM into stealthy ransomware staging infrastructure.
ETLM Assessment:
Affiliates are expected to deepen RMM portfolio rotation so that blocking one vendor only forces substitution among peer remote-administration products (High confidence). Allowlists that treat MeshAgent or Atera as inherently benign will continue to create blind spots once an adversary can rename and redeploy agents at scale. Defenders should inventory authorized RMM, alert on new agent installs outside change windows, and treat unexpected MeshCentral or multi-RMM coexistence as high-fidelity ransomware staging indicators.
Outbound Tunnel Services Paired with RMM to Convert Perimeter Blocks into Durable Internal Access
This activity highlights an evolution in ransomware persistence where commercial RMM is reinforced by outbound tunnel utilities that defeat inbound firewall assumptions. September 2026 Storm-2570 reporting detailed Cloudflare Tunnel services installed under LocalSystem alongside MeshAgent, plus ngrok exposure of RDP after policy and firewall changes enabled TCP 3389. The combined pattern turns compromised hosts into self-egressing management nodes, preserving hands-on-keyboard reach even when perimeter inbound remote access remains closed.
ETLM Assessment:
Ransomware operators are likely to standardize dual-channel persistence that pairs interactive RMM with always-on encrypted egress tunnels, reducing dependency on any single C2 domain (High confidence). Network controls that only restrict inbound VPN or RDP will remain insufficient against LocalSystem Cloudflare or ngrok services. Detection should correlate new tunnel service creation, unexpected cloudflared binaries, and RDP enablement scripts with unauthorized RMM installs.
Cloud Object-Store Utilities Industrializing Pre-Encryption Double Extortion
This campaign illustrates how ransomware data-theft tradecraft is evolving from ad-hoc archive uploads toward cloud-admin utilities that blend into legitimate transfer workflows. Across September 2026 Storm-2570 investigations, operators staged s5cmd with credential files to copy filtered business file types into attacker-controlled S3 buckets, while also using Rclone for continuous synchronization. By preferring tools designed for high-throughput object storage, affiliates compress the time between privileged access and publishable leak leverage before encryption begins.
ETLM Assessment:
Double-extortion pipelines are expected to keep favoring commodity cloud CLI tools that defenders already allow for backup and DevOps use, making pure malware-hash blocking ineffective (High confidence). Organizations should treat unexpected s5cmd or Rclone installs, new AWS credential files beside temporary binaries, and large outbound object-store transfers as ransomware-stage events even when no encryptor is yet present. Cloud egress monitoring and least-privilege storage credentials will become core ransomware controls rather than niche cloud-security concerns.
Privileged RMM Console Flaws Entering the Ransomware Access Inventory
This activity demonstrates the continued expansion of ransomware initial access from VPN appliances into privileged remote-management consoles that already hold administrative reach into customer estates. September 2026 reporting on Microsoft-tracked Storm-1175 activity (distinct from the Storm ransomware brand in the top-ten chart) highlighted exploitation of N-able N-central authentication bypass flaws in the CVE-2026-18556 / CVE-2026-18577 family, converting unpatched internet-facing RMM admin planes into full administrative footholds. Once console trust is obtained, follow-on use of SimpleHelp, AnyDesk, BYOVD, and NTDS.dit theft shows how RMM compromise collapses multiple later ransomware steps into a single privileged beachhead.
ETLM Assessment:
Access brokers and affiliates are expected to treat exposed RMM and remote-support consoles as durable access inventory comparable to VPN concentrators (Moderate confidence). Patching alone will not suffice if administrative sessions, API tokens, and downstream agent trusts survive after a hotfix. Enterprises and managed service providers (MSPs) should remove public exposure of management consoles, enforce phishing-resistant multi-factor authentication (MFA), and assume that a compromised RMM plane can seed ransomware across many tenants simultaneously.
From Single-Driver Killers to Multi-Kit and Callback-Zeroing BYOVD Tradecraft
This development highlights a technical evolution in ransomware defense evasion where Bring Your Own Vulnerable Driver (BYOVD) abuse is becoming modular, multi-kit, and quieter. September 2026 reporting by Beazley Security Labs (DFIR) described INC Ransom affiliates (tracked above as Incransom) deploying four distinct BYOVD packages in one intrusion, including wrapper utilities that overwrite endpoint detection and response (EDR) driver functions with RET gadgets, while Ontinue’s malware research on Lunex loaders compiled mid-September documented abuse of AMD PDFWKRNL.sys (CVE-2023-20598) to zero kernel notify callbacks after resolving offsets via Microsoft PDB downloads. The shift from terminating security processes toward leaving EDR running but blind raises the bar for integrity-based detection.
ETLM Assessment:
Ransomware and access ecosystems are expected to keep packaging BYOVD kits as reusable affiliate tooling, including help-dialog wrappers that lower skill barriers for operators (Moderate confidence). Vulnerable-driver blocklists that lag signed but abusable I/O drivers will remain a primary gap. Defenders should combine Microsoft vulnerable-driver blocking, Windows Defender Application Control (WDAC), hypervisor-protected code integrity (HVCI) where feasible, and hunts for unexpected driver service installs, PDB symbol downloads from non-debug hosts, and EDR health anomalies that indicate callback neutralization rather than process crash.
Ransomware Binaries Embedding Destructive Recovery-Environment Eviction
This activity demonstrates how ransomware impact capabilities are evolving beyond Volume Shadow Copy deletion into automated destruction of Windows recovery surfaces. Huntress analysis of a September Settra variant showed MeshAgent staging followed by ransomware child processes that invoked reagentc.exe /disable and diskpart scripts assessed to remove recovery partitions, while encrypting files with a .locked_wip extension. Embedding WinRE and recovery-partition eviction inside the encryptor itself shortens the path from privilege to irreversible restoration failure without relying on separate hands-on cleanup scripts.
ETLM Assessment:
Future ransomware builds are likely to standardize recovery-environment sabotage as a built-in impact module rather than an optional affiliate manual step (Moderate confidence). Backup strategies that depend on local WinRE, recovery partitions, or on-host restore media will become less trustworthy after compromise. Organizations should validate offline and immutable backups, monitor reagentc and diskpart abuse from uncommon parents, and treat unexpected recovery disablement as an early ransomware impact signal.
Sustained N-Day Fortinet Authentication Bypass Feeding Gunra Double Extortion
This activity highlights the ongoing industrialization of older Fortinet authentication-bypass flaws into active ransomware access pipelines. The joint #StopRansomware: Gunra advisory AA26-222A issued by the FBI, CISA, DC3, NSA, USSS, and the Republic of Korea’s National Police Agency (KNPA) warned that Gunra operators exploit FortiOS and FortiProxy issues, including CVE-2024-55591 and CVE-2025-24472, to obtain super-admin rights, bypass MFA assumptions on edge appliances, and progress into double-extortion operations. That advisory remained the primary public technical baseline for Gunra/Fortinet risk through September 2026. The evolutionary point is durability: patched-in-theory edge CVEs remain operational capital for RaaS affiliates whenever internet-facing Fortinet estates lag firmware upgrades.
ETLM Assessment:
Ransomware operators will continue harvesting residual exposure on Fortinet and peer edge platforms long after disclosure cycles end, because unpatched concentrators remain easier than developing new zero-days (High confidence). Emergency firmware upgrades without session invalidation and compromise assessment will leave previously established admin footholds intact. Continuous external scanning, MFA-proofing of SSL-VPN estates, and rapid credential rotation after Fortinet incident indicators remain essential ransomware hygiene.
Agentic Cloud Automation Extending Destructive Extortion into Azure Control Planes
This development highlights an emerging evolution of ransomware-adjacent impact from endpoint encryption toward high-speed, agent-driven destruction of cloud control-plane resources. Late-September 2026 reporting on Storm-3168 (JADEPUFFER) described highly automated Azure tenant abuse through compromised service principals, compressing hundreds of reconnaissance and destructive operations into short windows that deleted storage accounts, Key Vault material, and related services while attempting to disable backup and Site Recovery protections. Shared staging infrastructure with earlier large-language-model (LLM) agent campaigns shows how autonomous tooling can accelerate identity-driven cloud extortion without a classic on-prem encryptor.
ETLM Assessment:
Threat actors are expected to expand agentic automation against cloud identity and management APIs, prioritizing service principals and backup-lock bypasses that maximize irreversible business impact (Low-to-Moderate confidence). Cloud ransomware readiness must therefore include service-principal least privilege, continuous Azure Resource Manager (ARM) audit analytics, and immutable backup locks that cannot be disabled by the same compromised identity. Defenders should treat rapid bursts of destructive ARM operations as ransomware-class events even when no Windows encryptor hash is observed.
OVERALL RANSOMWARE TRENDS, SEPTEMBER 2026
BUSINESS IMPACT ANALYSIS
Industry studies of ransomware business impact provide useful context for interpreting the operational risk signaled by September 2026 activity. According to Cybereason’s Ransomware: The True Cost to Business study (2022), approximately 31% of surveyed organizations were forced to temporarily or permanently suspend operations following a ransomware attack. The same Cybereason study reported that nearly 40% of affected organizations laid off staff, and 35% experienced C-level executive resignations in the aftermath of an attack.
The financial and recovery burden is material even when no ransom is paid. Downtime, rebuild effort, legal and notification costs, and business interruption frequently exceed the ransom demand itself, and organizations that refuse to pay still carry the full cost of restoring and securing their systems.
EXTERNAL THREAT LANDSCAPE MANAGEMENT (ETLM) OVERVIEW
Impact Assessment
Ransomware remains a major threat to both organizations and individuals, locking critical data and demanding payment for its release. The consequences extend well beyond the ransom, often leading to costly recovery efforts, extended downtime, reputational harm, and potential regulatory fines. Such disruptions can destabilize operations and erode stakeholder trust. Addressing this growing risk demands a proactive cybersecurity posture and stronger collaboration between public and private sectors to build resilience against future attacks.
Victimology
Cybercriminals are increasingly targeting industries that manage vast amounts of sensitive data ranging from personal and financial information to proprietary assets. Sectors such as professional services, healthcare, real estate and construction, consumer goods and services, manufacturing, information technology, finance, and government remain high on the threat radar due to their complex and extensive digital infrastructures. Adversaries strategically exploit vulnerabilities in economically advanced regions, especially the United States, launching well-planned attacks designed to encrypt critical systems, disrupt production, and extract significant ransom payments.
OUTLOOK
Ransomware in September 2026 remains an enduring, multi-stage business threat. Although publicly disclosed incidents fell to 862 from August’s 1,170, the affiliate tradecraft documented this month — shared post-compromise toolchains, RMM and tunnel abuse, cloud-native exfiltration, modular BYOVD and built-in recovery sabotage — indicates, with high confidence, that operator capability has not diminished even where victim counts have. Resilience depends on identity and edge hardening, early lateral-movement detection, governance readiness, and preparation for both encryption and leak-driven outcomes.
