Q3 2026 CHECK-IN · THE ROAD TO DECEMBER
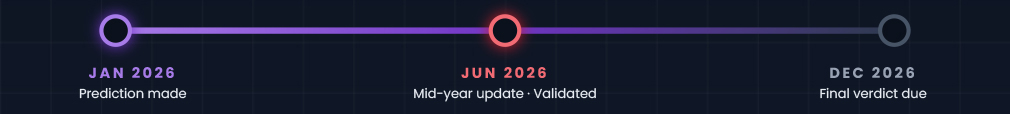
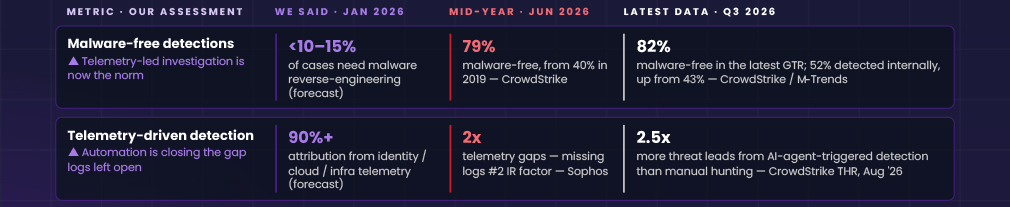
WHAT WE SAID (JAN 2026)
WHAT MID-YEAR SHOWED (JUN 2026)
WHAT TO EXPECT BY DECEMBER
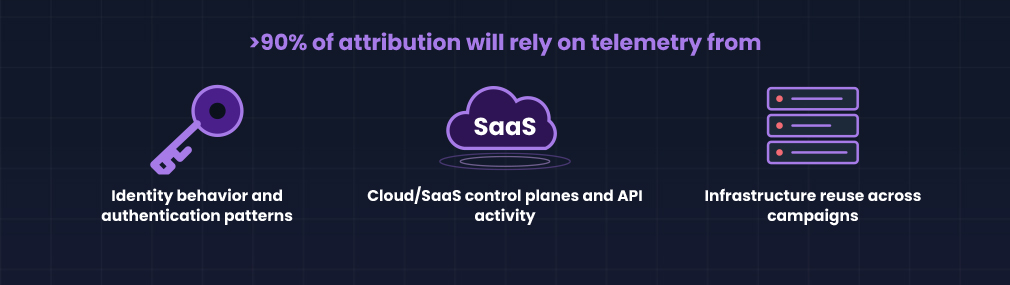
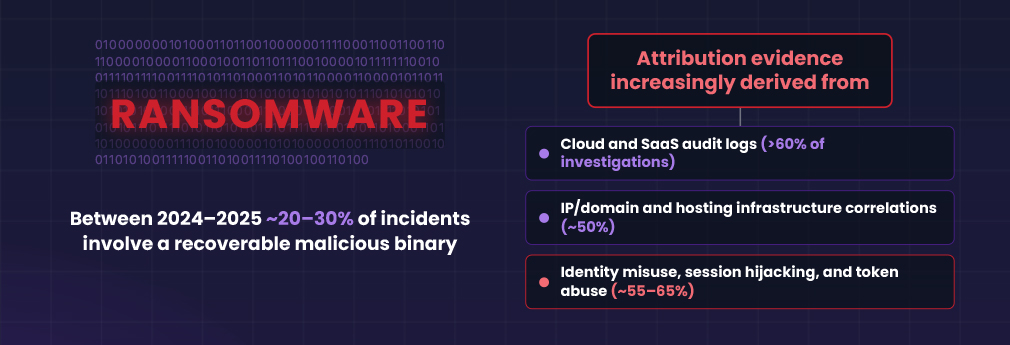
Infrastructure reuse drives attribution campaign linkage from hosting, domains and identity patterns rather than samples
Investigations have shifted decisively to identity, cloud and infrastructure telemetry. The binary is disposable; the evidence lives in logs.
OUR H2 OUTLOOK
We expect December to confirm telemetry-led attribution as the norm. The risk is not to the prediction but to defenders who are still deleting the only evidence they will get.
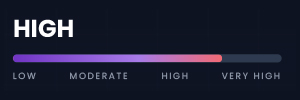
DECEMBER CONFIDENCE
NEXT: END-OF-YEAR VERDICT — DECEMBER 2026
Final verdicts on all 10 predictions, plus the first look at the Threat Horizon Series 2027.
MID-YEAR 2026 UPDATE · ROAD TO DECEMBER
WE PREDICTED (JAN 2026)
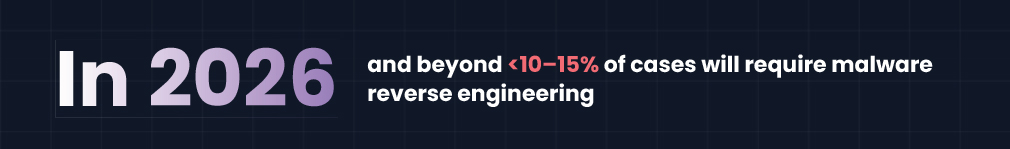
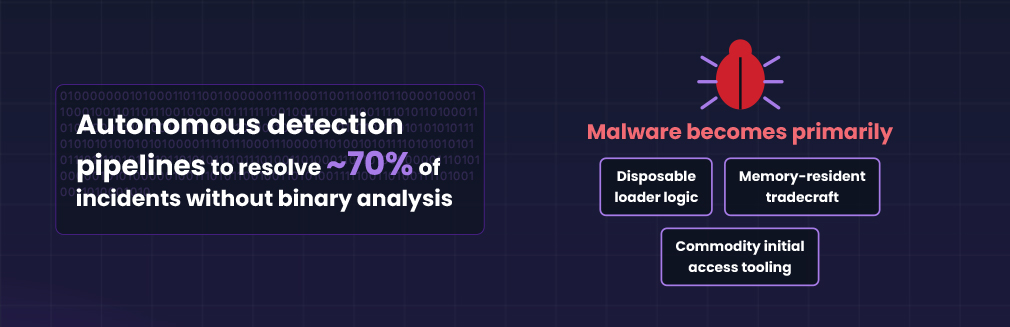
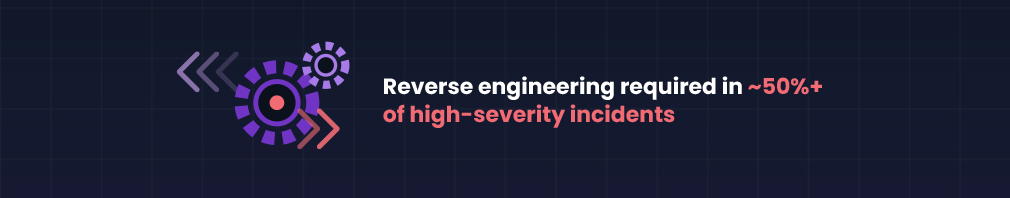
<10–15% of cases need malware RE 90%+ attribution from identity, cloud and infrastructure telemetry Malware becomes disposable loader logic
WHAT’S HAPPENING NOW
79% of detections are malware-free ~90% of IR cases involve identity loopholes Investigations hinge on identity/cloud logs Telemetry gaps doubled year over year
OUR UPDATED POSITION
On track. Investigations have shifted decisively to identity, cloud and infrastructure telemetry, while binaries are increasingly disposable. Log retention, API/audit visibility and infrastructure correlation are now the core of attribution. Treat identity and cloud telemetry as tier-1 forensic evidence and extend retention well beyond default windows.
IN THIS INSTALMENT WE EXPLORE · ROAD TO DECEMBER
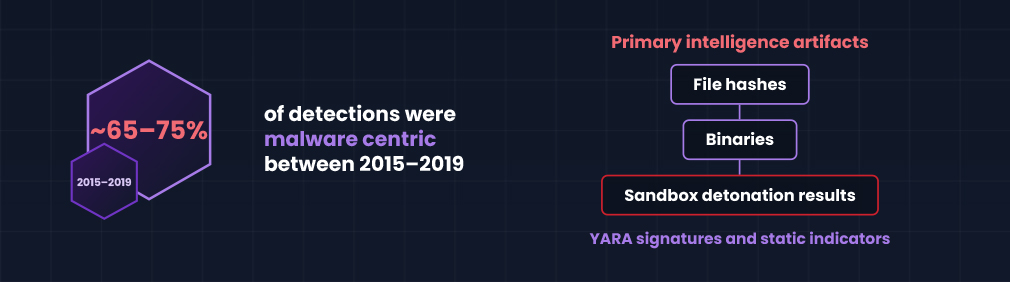
Analyzing past behaviour helps us assess Predictive Threat Intelligence
OUR PREDICTION · ROAD TO DECEMBER
Preemptive External Threat Landscape Management