
The highest month on record: 1,178 publicly claimed victims as multi-vendor edge access, hypervisor pivots and backup sabotage reshape the ransomware playbook
CYFIRMA tracked 1,178 publicly disclosed ransomware victims in October 2026, up 36.7% from September and the highest monthly total since tracking began. Qilin returned to the top of the rankings with 177 claimed victims, N0n rose from 18 to 142, and Professional Goods & Services, Manufacturing, Real Estate & Construction and Healthcare absorbed the most claims, with 44% of victims in the United States. Eight shifts in tradecraft, from multi-vendor edge access factories to offline VMDK credential theft and NAS factory resets, define the month’s playbook and the defensive priorities that follow.
BOTTOM LINE
Ransomware activity in October 2026 underscored the continued evolution of the threat landscape from isolated malware campaigns into a mature, service-driven criminal ecosystem capable of sustaining large-scale operations across multiple regions and sectors. With 1,178 publicly disclosed victims (+36.7% in September’s 862), October was the highest monthly total in CYFIRMA’s tracking to date, reflecting resilient ransomware-as-a-service (RaaS) operations and competition among leading brands.
Qilin led monthly activity with 177 claimed victims, followed by The Gentlemen (145), N0n (142), Akira (34), and NightSpire (34). Professional Goods & Services, Manufacturing, Real Estate & Construction, Healthcare, and Information Technology were the most-targeted industries; a further 113 victims (10%) were posted with the organization’s identity obfuscated. The United States accounted for 518 victims (44%), with 78 countries affected in total. Organizations should prioritize patching of internet-facing VPN, firewall, and backup consoles, including CVE-2026-0257 in PAN-OS GlobalProtect, harden hypervisor and backup administration planes, and monitor for the living-off-the-land staging activity described in Section 03.
| CLAIMED VICTIMS 1,178 +36.7% on September’s 862; highest month in CYFIRMA’s tracking |
LEADING OPERATOR Qilin 177 claimed victims; The Gentlemen 145, N0n 142 |
FASTEST RISER N0n 18 → 142, the largest single-month increase by any operator in 2026 |
| TOP INDUSTRY (CLAIMS) 170 Professional Goods & Services; then Manufacturing 123, Real Estate & Construction 122, Healthcare 120 |
MOST-TARGETED COUNTRY United States 518 claimed victims (44%); 78 countries affected |
OVERALL RISK High Moderate confidence; record volume on commodity access routes |
CONFIRMED
ASSESSED
NOT ESTABLISHED
CYFIRMA recommends three leadership priorities.
KEY FINDINGS
| # | PRIORITY | ACTION | OWNER |
| 1 | P1 · 7D | Patch or mitigate CVE-2026-0257 on all PAN-OS GlobalProtect portals and gateways; review GlobalProtect authentication logs since May 2026 for sessions that completed without MFA. | Network Security |
| 2 | P1 · 7D | Run one external exposure check across VPN, firewall, and backup consoles together, Cisco ASA/FTD, SonicWall, Veeam, against the vulnerabilities in CISA advisory AA26-293a; trigger a compromise review after any unexpected successful edge login. | Vulnerability Management |
| 3 | P1 · 7D | Alert on vCenter and ESXi security-flag changes (including execInstalledOnly being disabled) and on datastore access to domain-controller VMDK files outside backup windows; isolate management networks from general VPN users. | SOC / Virtualization |
| 4 | P1 · 7D | Separate NAS and backup administration credentials from domain credentials; alert on factory-reset and volume-delete actions; verify an immutable, identity-separated backup copy exists and restores. | Infrastructure / Backup |
| 5 | P2 · 7D | Enable Microsoft’s vulnerable-driver blocklist and WDAC or HVCI where feasible; hunt for driver-service installs (BootRepair.sys, ProcessMonitorDriver) paired with security tools stopping. | Endpoint Security |
| 6 | P2 · 7D | Allowlist approved remote-support and sync binaries; alert when Rclone, WinSCP, FileZilla, Backblaze or OneDrive clients execute on servers; correlate PsExec or WinRM spikes with edge compromise and backup tampering. | SOC |
4 NOVEMBER 2026 · TOP 10 TREND COMPARISON · NEW ENTRANTS AND EXITS
Top 10 trend comparison
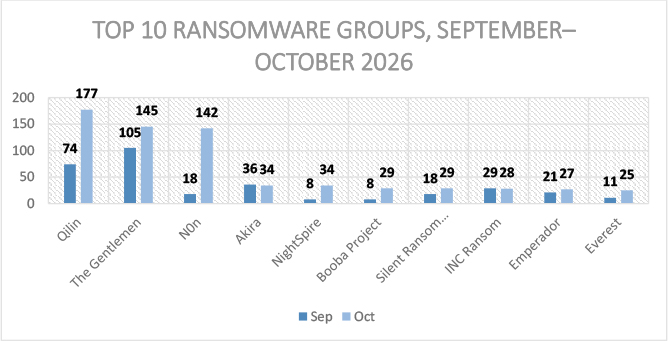
Figure 1. Top 10 ransomware groups by claimed victims, September-October 2026. Source: CYFIRMA leak-site monitoring, 1-31 October 2026
The September-October 2026 data indicates continued redistribution of ransomware activity. Leading operators included Qilin (74 → 177), The Gentlemen (105 → 145), N0n (18 → 142), Akira (36 → 34), NightSpire (8 → 34), Booba Project (8 → 29), Silent Ransom Group (18 → 29), INC Ransom (29 → 28), Emperador (21 → 27), and Everest (11 → 25). N0n’s rise from 18 to 142 claimed victims is the largest single-month increase by any operator this year; Akira and INC Ransom were the only top-ten operators whose counts did not rise. Overall, the RaaS ecosystem remains highly resilient, with operational capacity shifting among leaders and newcomers rather than signaling a sustained decline in the overall ransomware threat.
New entrants and exits
Three operators that each posted fewer than 20 claimed victims in September entered the October top ten: N0n (18 → 142), NightSpire (8 → 34), and Booba Project (8 → 29). Everest (11 → 25) and Emperador (21 → 27) also moved into the top ten. Together, the three fast risers added 171 claimed victims month on month, just over half of the 327-victim increase in overall volume, meaning October’s record was driven by new or returning brands rather than by growth among the established leaders.
4 NOVEMBER 2026 · MONTHLY VOLUME · INDUSTRY · GEOGRAPHY · ORGANIZATION SIZE
Monthly volume
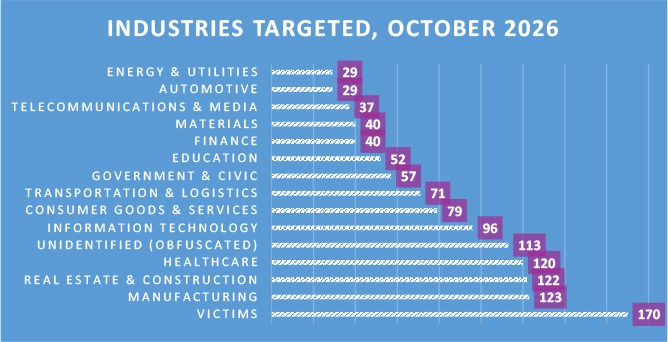
Figure 2. Publicly disclosed ransomware victims by month, 2024-2026. Source: CYFIRMA leak-site monitoring, 1-31 October 2026
Publicly disclosed incidents totaled 1,178 in October, compared with 862 in September and 1,170 in August, the highest monthly total in CYFIRMA’s tracking to date. Three of the four highest months on record have fallen in the second half of 2026. Multi-year volumes continue to show that RaaS operations remain active and adaptable across industries and regions.
Industry
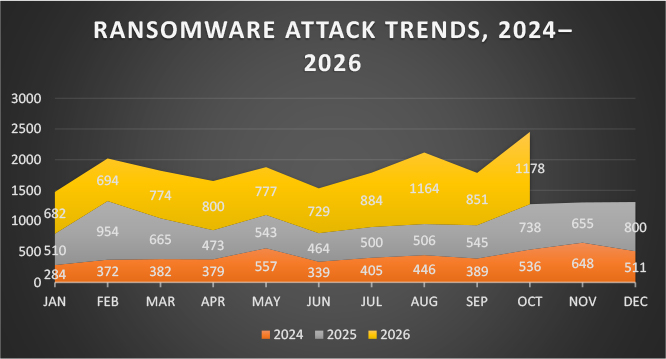
Figure 3. Claimed victims by industry, October 2026. Source: CYFIRMA leak-site monitoring, 1-31 October 2026
In October 2026, ransomware activity continued to focus on sectors where operational disruption and data theft maximize extortion leverage. Professional Goods & Services (170), Manufacturing (123), Real Estate & Construction (122), Healthcare (120), Information Technology (96), Consumer Goods & Services (79), Transportation & Logistics (71), Government & Civic (57), and Education (52) were the most-targeted industries. A further 113 victims (10%) were posted with the organization’s identity obfuscated and could not be assigned to a sector. Operators continue to prioritize industries where business disruption and sensitive-information exposure increase the likelihood of successful extortion.
Geography
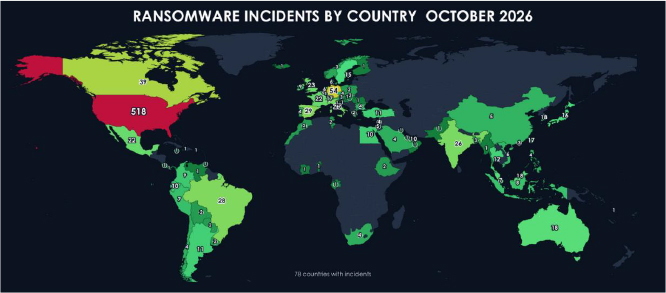
Figure 4. Claimed victims by country, October 2026. Source: CYFIRMA leak-site monitoring, 1-31 October 2026
Ransomware activity in October 2026 remained geographically concentrated in the United States, which recorded 518 publicly disclosed incidents (44% of the total). It was followed by Germany (54), Canada (39), Spain (29), Brazil (28), India (26), and Italy (25). In total, 78 identified countries were affected. Operators continue to prioritize digitally mature economies while maintaining a broad international footprint.
Organization size
CYFIRMA’s leak-site tracker does not currently record victim organization size, so no breakdown by employee or revenue band can be given for October 2026. Enrichment of the tracker to support this view is being assessed for future editions of RANSOM WATCH.
4 NOVEMBER 2026 · EIGHT SHIFTS IN TRADECRAFT · ETLM ASSESSMENT AND CONFIDENCE
This activity demonstrates a shift in ransomware initial access from chasing one freshly disclosed appliance bug toward keeping a reusable set of older edge flaws that can be scanned and exploited together. Until recently, many affiliates treated a single VPN or firewall CVE as a short window of opportunity. Late-October reporting on SafePay, including joint advisory AA26-293a published on 20 October 2026 by CISA, the FBI, and the U.S. Secret Service with German and UK law-enforcement partners, shows a more industrial model: stolen or phished credentials, privacy-VPN exits such as Mullvad, and automated exploitation across unpatched Cisco ASA and FTD flaws, Veeam backup weaknesses, and SonicWall access-control bugs. The real change is packaging. Unpatched internet-facing CVEs become durable access stock. Affiliates do not need the next zero-day if enough organizations still leave mixed VPN, firewall, and backup consoles exposed.
ETLM assessment. SafePay-style operators are expected to keep running multi-product edge harvest scripts against Cisco, SonicWall, and Veeam estates long after individual patches ship, because residual exposure still converts into ransomware footholds. Ticket-by-ticket CVE remediation will keep missing this model when scanners rotate among leftover flaws instead of camping on one disclosure. Organizations should run continuous external exposure checks across VPN, firewall, and backup consoles together, enforce stronger MFA on remote access, and trigger a compromise review after any unexpected successful edge login. CYFIRMA assesses with moderate confidence that this multi-vendor access model will persist through the next quarter; the assessment rests on a single joint advisory covering one operator.
This development highlights how ransomware operators are changing what they do after they get through a VPN. Earlier campaigns often used a stolen or bypassed VPN session mainly to reach Windows endpoints, dump credentials in the guest, and move over RDP or SMB. In mid-to-late October, Unit 42 reported (updated 20 October 2026) continued abuse of CVE-2026-0257, a PAN-OS GlobalProtect authentication bypass disclosed in May 2026 that lets attackers open GlobalProtect sessions without completing MFA. Qilin and INC Ransom were observed in that activity, and Unit 42 also noted public reporting that linked Settra ransomware operators to the same flaw, which it did not independently confirm. Once inside, some actors moved to vCenter, disabled ESXi hardening such as execInstalledOnly, and prepared credential theft from the virtualization layer. The VPN gateway is no longer just a way onto desktops. It is becoming a bridge into the management plane, where one compromise can matter more than many individual workstation footholds.
ETLM assessment. Qilin, INC Ransom, and peer affiliates are likely to keep treating MFA-bypass VPN sessions as on-ramps into vCenter and ESXi wherever GlobalProtect or similar gateways stay unpatched or weakly configured. Guest-only EDR will keep missing hypervisor hardening changes and management-plane pivots that never execute as noisy endpoint malware. Defenders should alert on vCenter and ESXi security-flag changes, isolate management networks from general VPN users, and escalate MFA-bypass VPN events as virtualization incidents rather than routine remote-access noise. CYFIRMA assesses with moderate confidence that this pattern will spread to other gateway products with authentication-bypass flaws.
This activity highlights a clear change in how ransomware crews steal domain credentials. The older pattern was live memory access, LSASS dumping, or on-host NTDS copies inside a running domain controller, which at least left process telemetry for EDR to catch. Unit 42’s October write-up described a different path: after ESXi hardening was disabled, custom tooling pulled secrets straight from a domain controller’s virtual disk without running the dump inside the guest OS. Sensors that only watch the live VM never see it. When the same operators also hit Veeam-related flaws to unlock backup credentials, the hypervisor and the backup plane start to look like interchangeable identity stores. The evolution is not that credentials are stolen. It is where they are taken from.
ETLM assessment. Ransomware crews are expected to keep refining offline VMDK and backup-store credential theft that never runs inside the guest operating system. Flat access to datastores, vCenter, and backup admin planes will keep creating identity blind spots even when endpoint EDR looks healthy on domain controllers. Hunt programs should correlate unexpected VMDK access, ESXi hardening disablement, and backup credential decryption with earlier edge or VPN compromise signals before encryption begins. CYFIRMA assesses with moderate confidence that offline credential extraction will become a standard step in hypervisor-focused intrusions over the next two quarters.
This pattern illustrates how ransomware groups are changing the way they kill recovery options. For years, the default move was deleting Volume Shadow Copy Service (VSS) snapshots and tinkering with recovery boot settings before encryption. October reporting on SafePay from U.S., German, and UK agencies (AA26-293a) shows operators going further: they stop VSS and factory-reset network-attached storage (NAS) backup appliances, wiping volumes that many teams still treat as their offline safety net. At the same time, data leaves the network through ordinary sync and transfer tools such as Rclone, the Backblaze command-line client, WinSCP, FileZilla, and sometimes OneDrive. The shift is a priority. Backup NAS admin planes are no longer a late cleanup. They are primary sabotage targets. A victim can lose leverage even when endpoint snapshots still look fine.
ETLM assessment. Operators will keep attacking the restore path as hard as production data, especially where NAS admin rights ride on the same domain credentials used elsewhere in the estate. Keeping more snapshots on a mutable backup appliance will not restore resilience once factory-reset and cloud-sync theft are part of the playbook. Use immutable and identity-separated backups, alert on NAS factory-reset or volume-delete actions, and watch for server-side Rclone, Backblaze, or peer sync tools during an intrusion window. CYFIRMA assesses with moderate confidence that backup-appliance sabotage will feature in a growing share of enterprise ransomware incidents.
This activity demonstrates a tooling change inside RaaS ecosystems: noisy piles of separate utilities are giving way to one framework that does most of the post-compromise work. Older affiliate kits often dropped Mimikatz, Rubeus, Chisel, scanners, and scripts side by side, which left a large footprint. Research published by Atos’s Threat Research Center on 19 October 2026, based on a leaked Eclipse ransomware C2 server discovered in early October, turned up Streamer, a Rust framework with a LuaJIT engine and more than 250 modules for credential theft, Active Directory work, Kerberos abuse, lateral movement, injection, and pivoting. The same stash held exploit scripts for VMware ESXi (CVE-2021-21974) and Veeam Backup Enterprise Manager (CVE-2024-29849), both adapted from public proof-of-concept code, and helpers that pull credentials out of Veeam SQL stores.
Classic dumpers were still there, but mostly as backups. One extensible binary can now replace a set of separate commodity tools and shorten the path from access to encryption readiness.
ETLM assessment. RaaS programs are expected to keep shipping affiliate-ready frameworks like Streamer that cut staging noise without losing Active Directory, credential, and pivoting capability. Hash detections aimed only at Mimikatz, Rubeus, or similar classics will miss native equivalents inside Rust and LuaJIT loaders. Cover the behaviors instead: AD attack primitives, unexpected high-module loaders, and co-located ESXi or Veeam exploit scripts on staging hosts. CYFIRMA assesses with low confidence that Streamer-style frameworks will be adopted beyond Eclipse within two quarters; the assessment rests on a single leaked server analyzed by one research team.
This development highlights how Bring Your Own Vulnerable Driver (BYOVD) abuse is becoming a shared product rather than a bespoke technique. Earlier intrusions often used one known bad driver tuned by a skilled operator. October threat reporting on The Gentlemen described abuse of Lenovo’s BootRepair.sys and Safetica’s ProcessMonitorDriver to kill security processes, while kits such as Terminator, AvNeutralizer, and EDRKillShifter kept circulating across multiple ransomware brands. That is the market change. Kernel-level EDR impairment is now something lower-skill affiliates can pick up before encryption, often alongside Defender tampering and log clearing. Signed but abusable drivers are becoming a recurring dependency for the ecosystem, not a rare advanced trick reserved for top-tier operators.
ETLM assessment. Vulnerable-driver loaders will keep circulating as reusable affiliate gear across The Gentlemen and peer ransomware brands, lowering the skill bar for pre-encryption EDR impairment. Estates that still allow known abusable signed drivers to load will stay soft even when user-mode EDR looks healthy. Turn on Microsoft’s vulnerable-driver blocklist and Windows Defender Application Control (WDAC) or hypervisor-protected code integrity (HVCI) where feasible, and hunt for unusual driver-service installs paired with security tools dying or going quiet before encryption. CYFIRMA assesses with moderate confidence that BYOVD tooling will continue to commoditize across RaaS affiliates.
This activity highlights a quieter change in how ransomware actors show up at enterprise VPN and firewall logins. Much SOC scoring still leans on coarse geography, ASN reputation, or obvious hostile hosting. October reporting on SafePay (AA26-293a) described logins arriving through Mullvad exits, paired with phished account profiles against Cisco remote-access surfaces, while automated exploitation ran in parallel. Those authentications look more like travel, contractor, or work-from-home traffic than a loud bulletproof ASN. The evolution is camouflage of the login itself. Edge compromise no longer has to arrive from known-hostile hosting ranges. That pushes detection toward MFA failures, impossible-travel checks, and first-seen devices, instead of destination reputation alone.
ETLM assessment. Operators will keep rotating privacy and residential VPN egress, including Mullvad-style exits, to make malicious edge logins look like ordinary remote work. Reputation-only VPN analytics will keep missing successful credential abuse when the source ASN looks consumer rather than hostile. Put weight on conditional access, phishing-resistant MFA, and alerts when admin or VPN logins arrive from privacy-VPN infrastructure during the same window as edge scanning or exploitation. CYFIRMA assesses with moderate confidence that privacy-VPN egress will become the default source profile for affiliate edge logins.
This pattern illustrates that October’s important change is not a brand-new lateral-movement malware family. It is the way legitimate administration and sync tools, living-off-the-land (LOTL) tradecraft, are now packaged as the normal ransomware business process. October reporting on SafePay (AA26-293a) repeatedly showed PsExec, WinRM, RDP, and commercial remote-support applications for hands-on control; ShareFinder and SharpShares for finding file shares; and Rclone, WinSCP, FileZilla, OneDrive, or Backblaze clients for bulk theft after defenses were weakened. Older playbooks mixed custom implants and dual-use tools more unevenly. The matured pattern keeps custom malware off stage until encryption, which shrinks the window where classic malware detections help. Defenders have to judge intent from context: sync tools on servers, sudden privileged remote execution, and backup sabotage showing up together.
ETLM assessment. Affiliates will keep preferring PsExec, WinRM, commercial remote-support applications, and cloud-sync clients because those tools blend into support workflows and delay hash-based detection until encryption. Hunting only for encryptors will miss the longer staging window where share discovery, privileged remote execution, and bulk sync already establish impact. Keep an allowlist of approved remote-support and sync binaries, alert when those tools appear on servers, and correlate PsExec or WinRM spikes with edge compromise and backup tampering. CYFIRMA assesses with high confidence that LOTL staging will remain the dominant pre-encryption pattern; it is corroborated across the joint advisory and multiple independent vendor reports.
4 NOVEMBER 2026 · BUSINESS IMPACT · IMPACT ASSESSMENT · VICTIMOLOGY
Business impact
Industry studies of ransomware business impact provide useful context for interpreting the operational risk signaled by October 2026 activity. According to Cybereason’s Ransomware: The True Cost to Business (2022) survey, approximately 31% of surveyed organizations were forced to temporarily or permanently suspend operations following a ransomware attack. The same study reported that nearly 40% of affected organizations laid off staff, and 35% experienced C-level executive resignations in the aftermath of an attack.
Financial and recovery burden remains material even when ransom is not paid: downtime, rebuild effort, legal and notification costs, and business interruption all accrue regardless of whether a demand is met, and organizations bear significant financial weight in restoring normal operations and securing their systems.
Impact assessment
Ransomware remains a major threat to both organizations and individuals, locking critical data and demanding payment for its release. The consequences extend well beyond the ransom, often leading to costly recovery efforts, extended downtime, reputational harm, and potential regulatory fines. Such disruptions can destabilize operations and erode stakeholder trust. Addressing this growing risk demands a proactive cybersecurity posture and stronger collaboration between public and private sectors to build resilience against future attacks.
Victimology
Cybercriminals are increasingly targeting industries that manage large volumes of sensitive data, ranging from personal and financial information to proprietary assets. Sectors such as professional services, manufacturing, real estate and construction, healthcare, information technology, consumer services, finance, and government remain high on the threat radar because of their complex and extensive digital infrastructures. The concentration of claimed victims in economically advanced regions, led by the United States, is consistent with operators selecting targets on expected ability to pay rather than on sector alone. Observed targeting points to a financially motivated selection model; this report infers that model from victim distribution rather than from direct knowledge of operator decision-making.
4 NOVEMBER 2026 · NOVEMBER AND THE QUARTER AHEAD · CONFIDENCE ON EVERY JUDGEMENT
4 NOVEMBER 2026 · STRATEGIC · MANAGEMENT · TACTICAL
The actions below are grouped by the level that owns them. Tactical items carry a suggested owner and priority; the six P1 and P2 items are repeated in the Executive Summary as the actions to take first.
Strategic
Management
Tactical
4 NOVEMBER 2026 · RANSOM WATCH · OCTOBER 2026
Ransomware in October 2026 remains an enduring, multi-stage business threat. On the intelligence available at the time of writing, 1,178 publicly disclosed incidents, the highest monthly total on record, Qilin’s return to the top of the rankings, and continued evolution in access, extortion, and affiliate models indicate that overall risk remains high even as brand rankings shift. Resilience depends on identity and edge hardening, early lateral-movement detection, governance readiness, and preparation for both encryption and leak-driven outcomes.
HANDLING · BASIS OF ASSESSMENT · WHAT TO WATCH NEXT · VERSION HISTORY · ABOUT CYFIRMA
HANDLING
TLP:CLEAR. This report is based primarily on CYFIRMA’s external ransomware monitoring, threat-actor leak-site observations, and public disclosures, and contains no customer-specific confidential information. It may be distributed without restriction.
BASIS OF ASSESSMENT
Figures are drawn from CYFIRMA’s monitoring of ransomware leak sites and public disclosures for 1-31 October 2026. Victim counts reflect claims made by the threat actors themselves and have not been independently verified; they may include re-posted, duplicated, disputed, or historical victims and exclude incidents resolved without public disclosure. They measure publicly claimed activity, not total ransomware incidence.
CYFIRMA THREAT INTELLIGENCE
[email protected] · Quote: RANSOM WATCH · Tracking Ransomware: October 2026
WHAT TO WATCH NEXT
N0n’s posting tempo in November; further operators observed using CVE-2026-0257; new vulnerable drivers added to Microsoft’s blocklist; adoption of Streamer-style frameworks by other RaaS programs; the November total against the 2026 average of roughly 850.
