
CYFIRMA has assessed N0n (also written n0n), a data-theft extortion group that launched a Tor leak site on 18 September 2026. Between 11 and 13 October 2026, the group posted 54 new entries, including 38 port, terminal, shipping and logistics organisations across 18 countries and territories, all posted within 23 minutes on 12 October. All 38 carry a single publication deadline of 19 October 2026, 13:27 UTC. Of the 38, 26 are in Asia, led by South Korea with 12 entries. In total, CYFIRMA has recorded 76 N0n leak-site entries, which correspond to an estimated 64 to 66 distinct organisations once duplicate anonymised posts are removed.
No listed organisation has publicly confirmed a breach. According to public reporting, the Korea Internet & Security Agency (KISA) is notifying named Korean port companies, and at least one firm has acknowledged receiving an intrusion notice. This is the first third-party signal that part of the maritime batch may reflect real intrusions. N0n claims to encrypt or destroy backups, but CYFIRMA has not identified an encryptor, ransom note, or other technical artefact linked to the group.
Assessment: N0n is a data-extortion actor with credible access to at least some listed victims (moderate confidence). Its claims of encryption, backup destruction, and network disruption are unverified (low confidence that the capability exists). Origin is unknown.
Recommended action: Organisations that exchange EDI with, or use systems from, a listed party should rotate shared EDI, SFTP, API and port community system credentials, enforce MFA on RDP, VPN, Citrix and cloud administration consoles, and monitor the N0n leak site and RSS feed through the 19 October 2026, 13:27 UTC deadline.
About This Report: This is a FIRST SIGHT report: an early assessment of an emerging threat, based on information collected up to 13 October 2026. CYFIRMA continues to monitor N0n’s leak site and related channels and will update this assessment, the indicators, and the threat hunting guidance as new details on the group’s victims, infrastructure, tooling, and TTPs emerge.
N0n moved from opportunistic, multi-sector targeting in September to a concentrated campaign against the maritime supply chain in October. The 12 October posting is the group’s largest single release and its first focused on one sector.
| Date (2026) | Event |
| 18 Sep | Leak site goes live with 10 entries, nine of them posted within five minutes. Victims include a US labour union, a business process outsourcing (BPO) provider supporting a payment platform, a Venezuelan internet service provider, a South American government ministry and a pharmaceutical subsidiary in Türkiye. |
| 20 to 30 Sep | Eight further entries, including a sports e-commerce platform, a retail software vendor, a marketing analytics SaaS vendor, a cloud hosting provider, a construction contractor, a mortgage lending platform and a US endocrinology practice. |
| 5 to 7 Oct | Anonymised “Company #” pre-listings begin (Company #1 to #3). A US IT managed services provider listed. |
| 11 Oct | 14 anonymised entries describing an estimated six organisations. Company #14 marked as having settled on 7 October. |
| 12 Oct | 38 maritime and logistics entries posted between 13:53 and 14:16, with a shared 19 October deadline. |
| 13 Oct | Two US businesses, a specialty retailer and a confectionery company, named after their anonymised deadlines expired. KISA notifies Korean victims, according to public reporting. A listed Korean steelmaker publicly describes its listing as a one-sided claim. |
| 19 Oct, 13:27 UTC | Scheduled publication of maritime batch data. |
This assessment is built on monitoring of the N0n leak site and relevant context via our DeCYFIR platform. Each data point is graded as confirmed (two or more independent observers), actor claim (leak-site text only), or analyst inference.
Leak Site and Extortion Infrastructure
The leak site uses the tagline “no js | no mercy” and runs without JavaScript or a CAPTCHA. It has Active, Leaked, and Honor sections, offers stolen data as .zip and .torrent downloads, and publishes an RSS feed. Victims enter a private negotiation room using a personal key.
Listing Behaviour
Listings follow a consistent English template: sector and country, claimed data, an operational claim, and a status with a UTC deadline. Status labels are ACTIVE, PENDING EXPOSURE, NOT PAID / EXPOSED and HONORED. Since 5 October, N0n has posted anonymised “Company #” entries describing only sector and location, then named the victim after the deadline. This pattern is confirmed for two US businesses. The tactic adds pressure on victims and inflates entry counts: the 14 anonymised entries posted on 11 October appear to describe about six organisations, several of them listed two to four times.
Pseudonym numbering is non-sequential in CYFIRMA’s collection. Company #6 to #13 and #15 to #18 have not been observed. This may indicate entries removed after settlement or posted and withdrawn between collection intervals (analyst inference, low confidence).
The tone of the claims has changed. September listings claimed operational disruption, such as a “network blackout” at a BPO provider and severed network traffic at an ISP. The October maritime listings claim only data categories and make no disruption claims.
Capabilities
| Tactic | ID | Technique | Evidence basis |
| Initial Access | T1078 | Valid Accounts | Assessed as the most probable vector. No stealer family or access artefact identified. |
| Lateral Movement | T1021.001 | Remote Desktop Protocol | Assessed. No artefacts identified. |
| Collection | T1074 | Data Staged | Consistent with listing contents. |
| Exfiltration | Not determined | Not determined | No exfiltration tooling identified. |
| Impact | T1657 | Financial Theft (extortion) | Supported by leak-site demands and the claimed payment. |
| Impact | T1486, T1490 | Data Encrypted for Impact; Inhibit System Recovery | Actor claims only. No encryptor or ransom note identified. |
Encryption Capability
N0n’s listings claim that backups and shadow copies were encrypted or destroyed (a retail software vendor and an IT services provider) and that victim networks were taken offline (a BPO provider, an ISP, a government ministry, and a cloud hosting provider). CYFIRMA has not identified an encryptor, file hash, ransom note, or encrypted-file extension associated with N0n. CYFIRMA assesses with low confidence that N0n has deployed encryption and treats the group as a data-extortion actor. Mappings of N0n to T1486 should be treated as actor-claimed until a sample is recovered.
Initial Access
Use of valid credentials, most plausibly harvested by infostealer malware, is the most probable initial access vector given the spread of small and large victims across unrelated sectors and the absence of any shared exploited product. No artefact confirms this.
| Question | Assessment | Confidence |
| Origin | Unknown. No language, infrastructure, or forum evidence ties N0n to a country. The leak site is in English. The listing of an Uzbek company (a CIS member state) argues weakly against a Russian-speaking criminal profile. | Low |
| RaaS or affiliates | No recruitment posts, affiliate panel, or forum advertising observed. | Low |
| Links to known groups | No shared infrastructure, code, or template overlap observed. The bulk-posting pattern resembles 0APT, whose early-2026 victim list was shown to be largely fabricated. This is an analogy, not a link. | Low |
| Real access to victims | KISA’s reported notifications and one Korean firm’s acknowledged intrusion notice support real access for part of the Korean set. | Moderate |
| Shared supplier compromise | The batch includes port IT intermediaries: port community system operators in the Middle East and South Korea, a port logistics IT provider in Indonesia, and a port consultancy in Germany. EDI data naming many parties could come from a single hub compromise rather than 38 separate intrusions. | Low (hypothesis) |
CYFIRMA has recorded 76 N0n leak-site entries between 18 September and 13 October 2026. After removing anonymised entries that duplicate other listings, the dataset represents an estimated 66 distinct organisations, or 64 if two further pairs (Company #2 and #14; Company #3 and the IT managed services provider listed on 7 October) are also duplicates. The analysis below uses the 66-organisation set unless stated.
Posting Cadence
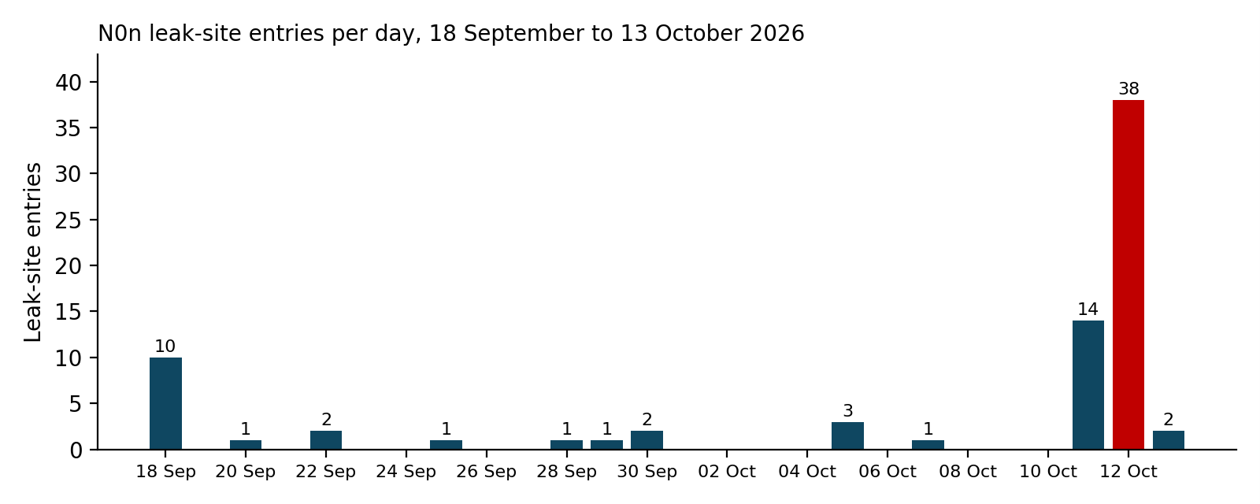
Figure 1: N0n leak-site entries per day (all 76 entries)
Activity came in three bursts: the 18 September launch (10 entries), the 11 October anonymised wave (14 entries) and the 12 October maritime batch (38 entries). Between bursts, N0n posted one to three entries on scattered days. In total, 52 of 76 entries (68%) were posted on 11 and 12 October.
Industries
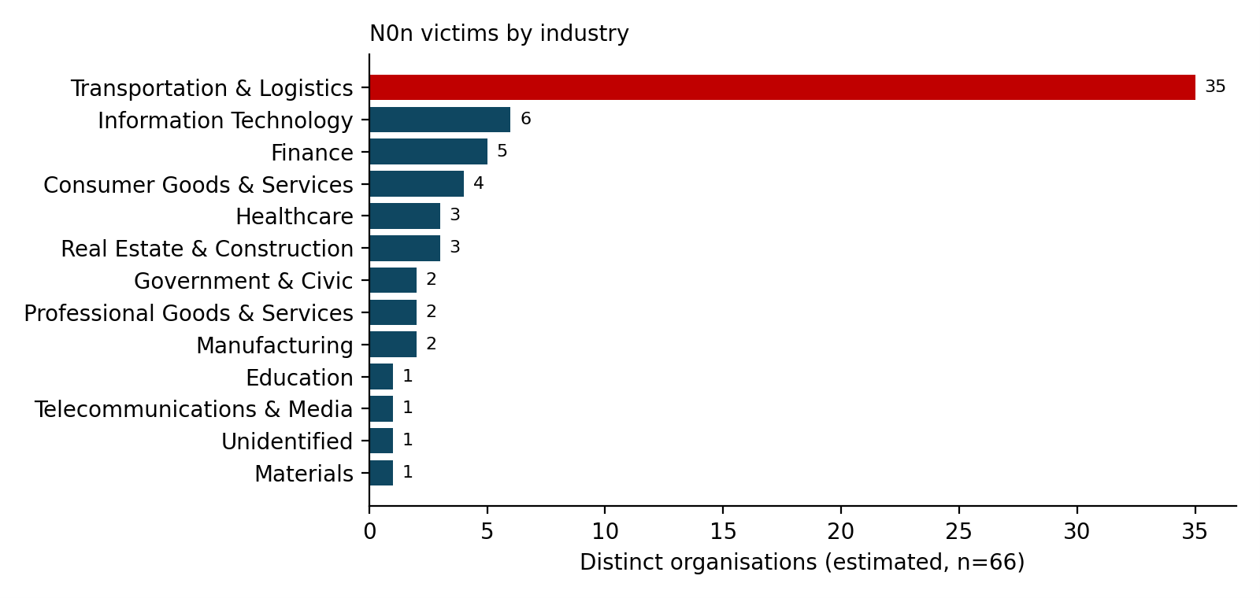
Figure 2: N0n victims by industry (estimated 66 distinct organisations)
Transportation & Logistics accounts for 35 organisations (53%), of which 33 are classified as Maritime Logistics. Including a port machinery manufacturer, a shipbuilder and a steelmaker, all posted in the maritime batch, 38 victims (58%) sit in the maritime supply chain. Within the batch, terminal and port operators form the largest group (13, including eight container terminal operators), followed by shipping lines and ship operators (10), port and ship agencies and logistics providers (6), port IT and terminal systems providers (4), maritime services firms (2) and three manufacturers (steel, shipbuilding and port machinery). The four port IT and terminal systems providers carry the widest downstream risk, because each serves many terminals, carriers and agents.
Outside the batch, victims are spread thinly across 23 sectors, with no sector holding more than two organisations, which is consistent with opportunistic access rather than sector targeting.
Geographies
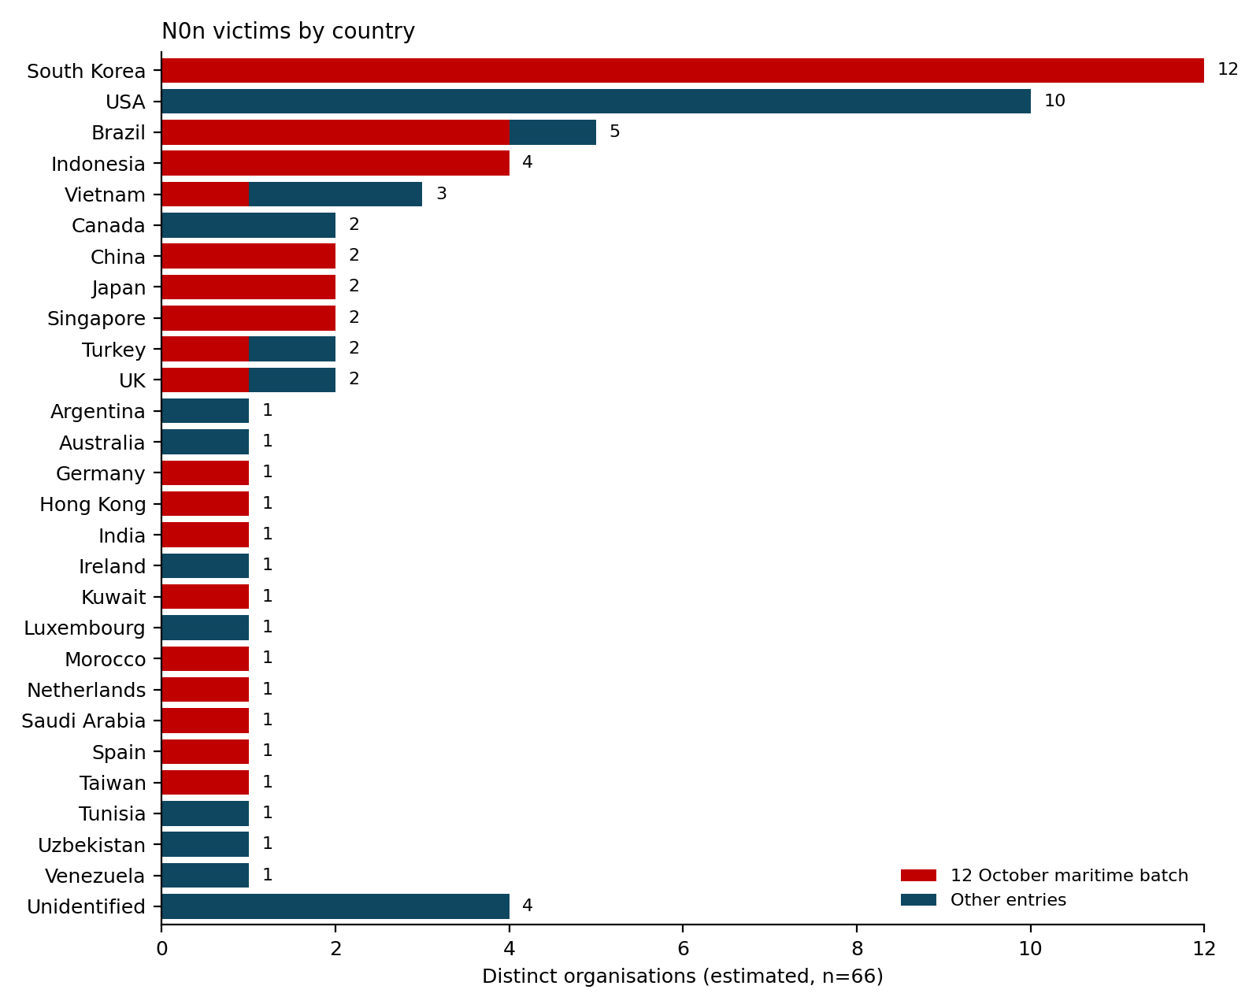
Figure 3: N0n victims by country (estimated 66 distinct organisations)
Victims are located in 27 named countries and territories, with four further victims whose country was with held.
The geographic profile changed with the maritime batch. Outside the batch, victims are mainly in the Americas (15 of 24 with a known country), led by the United States with 10 organisations spanning a labour union, e-commerce, SaaS, healthcare, managed IT services, investment and small businesses. Before deduplication, the US accounts for 19 entries, because most anonymised repeat listings describe US businesses. The maritime batch is Asia-heavy: 26 of its 38 victims are in Asia, 18 of them in East Asia. As a result, Asia now holds 29 of the 62 victims with a known country (47%), against 19 in the Americas and nine in Europe.
South Korea is the clearest concentration. All 12 Korean victims are in the batch and cover nearly every layer of a port ecosystem: container and port terminals, an inland container depot, ship management, ferry, tanker and dry bulk operators, a ship agency, a logistics company and a port community IT provider, plus a steel manufacturer. A spread this broad within one country fits either deliberate targeting of the Korean port sector or a single upstream compromise, such as a shared port IT platform. Indonesia (4) and Brazil (4) follow. The Indonesian victims are two port agencies, a coastal shipping operator and a port logistics IT provider; the Brazilian victims are three terminal or port operators and a terminal systems provider. Elsewhere the batch is thin: one or two organisations each in Japan, China, Singapore, Taiwan, Hong Kong, Vietnam and India, five in Europe including Türkiye, two in the Gulf and one in Morocco.
Technologies
Technologies named in N0n listings or assessed as relevant to its access and targeting: terminal operating systems, EDI messaging (manifests, bookings, gate movements), port community systems, remote access services (RDP, VPN, Citrix), cloud hosting and accounting software.
Data Exposure and Likely Misuse
All data categories below are actor claims taken from leak-site listings. CYFIRMA has not yet validated the contents of published N0n data.
| Claimed data | Victim types | Likely downstream misuse |
| EDI archives (manifests, bookings, gate movements) | Container terminals in Brazil and Vietnam; container shipping lines in China and Taiwan | Mapping of cargo contents and movements, which could support cargo theft, smuggling, and targeting of trading partners. |
| TOS database scripts and configuration | Port and terminal operators in Brazil and South Korea | Reconnaissance for follow-on intrusion into terminal systems. |
| Invoices, settlements, banking correspondence templates | Korean steelmaker, ship agency and terminal operator; Japanese ferry operator | Invoice fraud and business email compromise against shipping counterparties. |
| Credentials | Korean ferry operator (plaintext staff credentials); US specialty retailer (577 accounts) | Credential stuffing and re-entry into victim networks. |
| Infrastructure and vulnerability records | Korean logistics company; BPO provider (AD and PKI map) | Targeted intrusion by N0n or third parties. |
| Personal and patient data | US endocrinology practice, US labour union, Canadian mortgage platform | Identity fraud, phishing, and regulatory exposure for the victim. |
Affected parties extend beyond the listed victims to shippers, consignees, carriers and agents named in EDI records and invoices, and to customers, patients and members whose data the victims held.
Concern is highest for three groups.
Remote access that accepts stolen single-factor credentials raises exposure in all three groups. Outside the maritime sector, N0n’s September and early-October entries show that healthcare, financial services, managed service providers, SaaS vendors and small businesses, mainly in the US and Canada, with single cases in the UK and Australia, remain exposed to opportunistic targeting.
Exposure depends on three factors: whether your records sit in EDI archives or invoice data held by listed parties; whether employee credentials appear in infostealer logs; and whether RDP, VPN, Citrix or cloud admin consoles accept single-factor logins. The data publication scheduled for 19 October will show what N0n actually holds and is the main test of whether the maritime claims are real.
| Type | Indicator | Notes |
| Onion domain | nongzecboljwv3yfndkggsybsglfrkffw7bvk2zemuteoxe6etpusnad.onion | N0n leak site. |
CYFIRMA has not identified file hashes, IP addresses, ransom notes, email addresses, or Tox IDs associated with N0n. No N0n malware sample is available. The rules in the next section are therefore threat hunting rules, not N0n detection signatures.
No Non technique has yet been confirmed through technical artefacts. The rules below target techniques CYFIRMA assesses N0n is likely to use, based on its leak-site claims and common data-extortion tradecraft. They are intended for proactive threat hunting and prevention, so a match indicates activity worth investigating, not N0n involvement. None has been validated against N0n activity, and all need local testing and tuning for false positives.
Sigma Rules: Shadow Copy and Backup Catalogue Deletion (T1490)
title: Shadow Copy or Backup Catalogue Deletion
id: 6f1d2c9e-3b7a-4e52-9d1f-8a4c0b2e7d31
status: experimental
description: Hunts for deletion of volume shadow copies or the Windows backup catalogue. N0n claims to destroy backups, but this is not confirmed by artefacts.
author: CYFIRMA Research
date: 2026-10-14
tags:
– attack.impact
– attack.t1490
logsource:
category: process_creation
product: windows
detection:
selection_vssadmin:
Image|endswith: ‘\vssadmin.exe’
CommandLine|contains|all:
– ‘delete’
– ‘shadows’
selection_wmic:
Image|endswith: ‘\WMIC.exe’
CommandLine|contains|all:
– ‘shadowcopy’
– ‘delete’
selection_wbadmin:
Image|endswith: ‘\wbadmin.exe’
CommandLine|contains|all:
– ‘delete’
– ‘catalog’
condition: 1 of selection_*
falsepositives:
– Administrative backup maintenance
level: high
Sigma Rules: Rclone Execution (T1567.002)
title: Rclone Execution on Windows Host
id: 2b8e4a71-c05d-4f3e-a9b6-71d3e5f0c842
status: experimental
description: Hunts for rclone, a tool commonly used by extortion groups for bulk exfiltration to cloud storage. N0n exfiltration tooling is unknown.
author: CYFIRMA Research
date: 2026-10-14
tags:
– attack.exfiltration
– attack.t1567.002
logsource:
category: process_creation
product: windows
detection:
selection_image:
Image|endswith: ‘\rclone.exe’
selection_pe:
OriginalFileName: ‘rclone.exe’
selection_desc:
Description: ‘Rsync for cloud storage’
condition: 1 of selection_*
falsepositives:
– Sanctioned backup or migration jobs
level: high
Sigma Rules: RDP Logon from Public Address (T1021.001, T1078)
title: Successful RDP Logon from Non-Private IP Address
id: 9c3f7d10-4e28-4b6a-8f05-d2a1b6e94c57
status: experimental
description: Hunts for successful RemoteInteractive logons from public IP addresses, consistent with use of stolen credentials over exposed RDP, an assessed but unconfirmed N0n access vector.
author: CYFIRMA Research
date: 2026-10-14
tags:
– attack.initial_access
– attack.t1078
– attack.lateral_movement
– attack.t1021.001
logsource:
product: windows
service: security
detection:
selection:
EventID: 4624
LogonType: 10
filter_private:
IpAddress|cidr:
– ‘10.0.0.0/8’
– ‘172.16.0.0/12’
– ‘192.168.0.0/16’
– ‘127.0.0.0/8’
– ‘::1/128’
– ‘fe80::/10’
condition: selection and not filter_private
falsepositives:
– Approved remote access through jump hosts with public addresses
level: medium
The YARA rules below scan files rather than logs. The first matches N0n’s leak-site address and tagline, which would appear in extortion notes, emails or saved web pages, and is the only rule tied to a known N0n artefact. The other three hunt for tooling linked to the likely techniques above: shadow copy and backup deletion, and bulk exfiltration with rclone.
YARA Rules: N0n Leak-Site Reference (infrastructure strings)
rule N0n_LeakSite_Reference
{
meta:
description = “Files referencing the N0n leak-site onion address or its tagline, such as extortion notes, emails or saved web pages”
author = “CYFIRMA Research”
date = “2026-10-14”
id = “725a81ae-d6e9-4bd2-b5ec-32194c53ba88”
reference = “CYFIRMA FIRST SIGHT: N0n Extortion Group Targets Global Shipping”
scope = “Known N0n infrastructure strings, not malware”
confidence = “high for $onion, medium for $tagline”
strings:
$onion = “nongzecboljwv3yfndkggsybsglfrkffw7bvk2zemuteoxe6etpusnad” ascii wide nocase
$tagline = /no\s?js\s?\|\s?no\s?mercy/ ascii wide nocase
condition:
filesize < 20MB and any of them
}
YARA Rules: Shadow Copy and Backup Deletion Commands (T1490)
rule Hunt_Shadow_Copy_And_Backup_Deletion_Commands
{
meta:
description = “Scripts or binaries containing two or more shadow copy, backup catalogue or recovery deletion commands, a technique N0n claims but has not been confirmed to use”
author = “CYFIRMA Research”
date = “2026-10-14”
id = “5cfd1f23-5451-46f8-83e8-a1b225f9880a”
mitre_attack = “T1490”
scope = “Threat hunting for a likely technique, not confirmed N0n activity”
false_positives = “Administrative backup maintenance scripts; legitimate security tools that embed these commands”
strings:
$c1 = /vssadmin(\.exe)?”?\s+delete\s+shadows/ ascii wide nocase
$c2 = /vssadmin(\.exe)?”?\s+resize\s+shadowstorage/ ascii wide nocase
$c3 = /wmic(\.exe)?”?\s+shadowcopy\s+delete/ ascii wide nocase
$c4 = /wbadmin(\.exe)?”?\s+delete\s+(catalog|systemstatebackup|backup)/ ascii wide nocase
$c5 = /bcdedit(\.exe)?”?\s+\/set\s+\{default\}\s+recoveryenabled\s+no/ ascii wide nocase
$ps1 = “Win32_ShadowCopy” ascii wide nocase
$ps2 = “Remove-CimInstance” ascii wide nocase
$ps3 = “Remove-WmiObject” ascii wide nocase
$ps4 = “.Delete()” ascii wide nocase
condition:
filesize < 10MB and
(
2 of ($c*) or
($ps1 and 1 of ($ps2, $ps3, $ps4))
)
}
YARA Rules: Rclone Binary (T1567.002)
rule Hunt_Rclone_Binary
{
meta:
description = “Rclone executables, including renamed copies; rclone is commonly used by extortion groups for bulk exfiltration to cloud storage”
author = “CYFIRMA Research”
date = “2026-10-14”
id = “938b7207-8a0d-463f-8b15-58d12991845d”
mitre_attack = “T1567.002”
scope = “Threat hunting for a likely technique, not confirmed N0n activity. N0n exfiltration tooling is unknown”
false_positives = “Sanctioned backup or migration tooling”
strings:
$s1 = “github.com/rclone/rclone” ascii
$s2 = “Rsync for cloud storage” ascii wide
$s3 = “rclone.org” ascii
condition:
(
uint16(0) == 0x5A4D or
uint32(0) == 0x464C457F or
uint32(0) == 0xFEEDFACF or
uint32(0) == 0xCFFAEDFE
)
and 2 of them
}
YARA Rules: Rclone Configuration with Cloud Remote (T1567.002)
rule Hunt_Rclone_Config_With_Cloud_Remote
{
meta:
description = “Rclone configuration files defining a cloud or file-transfer remote, or an encrypted rclone configuration”
author = “CYFIRMA Research”
date = “2026-10-14”
id = “6852333e-0590-4a34-aa31-c4c3ca1a2591”
mitre_attack = “T1567.002”
scope = “Threat hunting for a likely technique, not confirmed N0n activity”
false_positives = “Legitimate rclone use by administrators or developers”
strings:
$type = /\ntype\s?=\s?(mega|s3|ftp|sftp|pcloud|dropbox|drive|onedrive|b2|webdav|box|swift|azureblob|putio)\b/ ascii nocase
$key = /\n(user|pass|access_key_id|secret_access_key|token|host|endpoint|account)\s?=\s?\S/ ascii nocase
$enc = “RCLONE_ENCRYPT_V0:” ascii
condition:
filesize < 64KB and (($type and $key) or $enc)
}
All 76 leak-site entries recorded by CYFIRMA, in posting order. Victims are described by type. Anonymised “Company #” entries are shown with the actor’s label, including those assessed as duplicates.
| Victim profile | Posted | Country | Industry | Sector |
| Labour union | 18 Sep 15:22 | USA | Government & Civic | Labor & Social Services (Union) |
| Online betting operator | 18 Sep 15:23 | Vietnam | Consumer Goods & Services | Events & Entertainment Services |
| Education centre operator | 18 Sep 15:23 | Vietnam | Education | Educational Technology & Learning Platforms |
| Legal services firm | 18 Sep 15:24 | Brazil | Professional Goods & Services | Legal Services |
| Digital securities platform | 18 Sep 15:25 | Luxembourg | Finance | FinTech |
| Pharmaceutical company subsidiary | 18 Sep 15:25 | Türkiye | Healthcare | Pharmaceuticals & Biotechnology |
| Investment firm | 18 Sep 15:26 | USA | Finance | Investment Firm |
| National government ministry | 18 Sep 15:26 | Argentina | Government & Civic | National Government & Executive Bodies |
| BPO provider (payment platform support) | 18 Sep 15:27 | Tunisia | Professional Goods & Services | Business Process Outsourcing (BPO) |
| Internet service provider | 18 Sep 19:51 | Venezuela | Telecommunications & Media | Internet Service Providers (ISPs) |
| Sports e-commerce platform | 20 Sep 02:51 | USA | Consumer Goods & Services | Retail – E-Commerce & Direct-to-Consumer |
| Retail back-office software vendor | 22 Sep 01:51 | Uzbekistan | Information Technology | Vertical Industry Software |
| IT and document processing services provider | 22 Sep 17:22 | Unidentified | Information Technology | Document & Workflow Management |
| Marketing analytics platform | 25 Sep 03:21 | USA | Information Technology | Digital Marketing Technology (MarTech) |
| Cloud hosting provider | 28 Sep 05:51 | Ireland | Information Technology | Cloud Service Providers (IaaS PaaS SaaS) |
| Facade contractor | 29 Sep 05:51 | UK | Real Estate & Construction | Specialty Trade Contractors |
| Commercial mortgage lending platform | 30 Sep 12:52 | Canada | Finance | Mortgage Brokerage |
| Endocrinology practice | 30 Sep 22:53 | USA | Healthcare | Specialized Medicine |
| Company #1 (anonymised) | 05 Oct 09:53 | Unidentified | Unidentified | Unidentified |
| Company #2 (anonymised) | 05 Oct 09:54 | Unidentified | Finance | Not specified |
| Company #3 (anonymised) | 05 Oct 09:54 | Unidentified | Information Technology | IT Consulting & Managed Services |
| IT managed services provider | 07 Oct 05:51 | USA | Information Technology | IT Consulting & Managed Services |
| Company #4 (anonymised) | 11 Oct 07:23 | USA | Real Estate & Construction | Architecture & Design Firms |
| Company #5 (anonymised) | 11 Oct 08:23 | USA | Real Estate & Construction | Building Systems Controls & Facility Services |
| Company #25 (anonymised) | 11 Oct 14:22 | USA | Consumer Goods & Services | Food & Beverage |
| Company #26 (anonymised) | 11 Oct 14:23 | USA | Consumer Goods & Services | Not specified |
| Company #27 (anonymised) | 11 Oct 14:23 | Australia | Healthcare | Specialized Medicine |
| Company #28 (anonymised) | 11 Oct 14:24 | USA | Real Estate & Construction | Architecture & Design Firms |
| Company #29 (anonymised) | 11 Oct 14:24 | USA | Real Estate & Construction | Building Systems Controls & Facility Services |
| Company #14 (anonymised) | 11 Oct 18:53 | Canada | Finance | Not specified |
| Company #19 (anonymised) | 11 Oct 18:53 | USA | Consumer Goods & Services | Food & Beverage |
| Company #20 (anonymised) | 11 Oct 18:54 | USA | Consumer Goods & Services | Not specified |
| Company #21 (anonymised) | 11 Oct 18:55 | Australia | Healthcare | Specialized Medicine |
| Company #22 (anonymised) | 11 Oct 18:55 | USA | Real Estate & Construction | Architecture & Design Firms |
| Company #23 (anonymised) | 11 Oct 18:56 | USA | Real Estate & Construction | Building Systems Controls & Facility Services |
| Company #24 (anonymised) | 11 Oct 20:53 | USA | Real Estate & Construction | Building Systems Controls & Facility Services |
| Container terminal operator | 12 Oct 13:53 | Vietnam | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 13:54 | South Korea | Transportation & Logistics | Maritime Logistics |
| Port logistics IT provider | 12 Oct 13:55 | Indonesia | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 13:55 | Morocco | Transportation & Logistics | Maritime Logistics |
| Ferry and RoRo operator | 12 Oct 13:56 | Japan | Transportation & Logistics | Maritime Logistics |
| Ship management company | 12 Oct 13:57 | South Korea | Transportation & Logistics | Maritime Logistics |
| Terminal systems provider | 12 Oct 13:57 | Brazil | Transportation & Logistics | Maritime Logistics |
| Ferry operator | 12 Oct 13:58 | South Korea | Transportation & Logistics | Maritime Logistics |
| Inland container depot operator | 12 Oct 13:59 | South Korea | Transportation & Logistics | Maritime Logistics |
| Marine surveying and inspection firm | 12 Oct 13:59 | UK | Transportation & Logistics | Maritime Logistics |
| Logistics company | 12 Oct 14:00 | South Korea | Transportation & Logistics | Integrated Logistics |
| Oil tanker operator | 12 Oct 14:01 | South Korea | Transportation & Logistics | Maritime Logistics |
| Port agency | 12 Oct 14:01 | Indonesia | Transportation & Logistics | Maritime Logistics |
| Ship agency | 12 Oct 14:02 | South Korea | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 14:03 | Spain | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 14:03 | India | Transportation & Logistics | Maritime Logistics |
| Steel manufacturer | 12 Oct 14:04 | South Korea | Materials | Steel & Iron Products |
| Coastal shipping operator | 12 Oct 14:05 | Indonesia | Transportation & Logistics | Maritime Logistics |
| Port community IT provider | 12 Oct 14:05 | South Korea | Transportation & Logistics | Maritime Logistics |
| Port IT services provider | 12 Oct 14:06 | Kuwait | Transportation & Logistics | Maritime Logistics |
| Industrial port operator | 12 Oct 14:06 | Saudi Arabia | Transportation & Logistics | Maritime Logistics |
| Port terminal operator | 12 Oct 14:07 | Brazil | Transportation & Logistics | Maritime Logistics |
| Commodity processing and logistics group | 12 Oct 14:08 | Singapore | Transportation & Logistics | Maritime Logistics |
| Port consulting firm | 12 Oct 14:08 | Germany | Transportation & Logistics | Maritime Logistics |
| Container shipping line | 12 Oct 14:09 | Taiwan | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 14:09 | South Korea | Transportation & Logistics | Maritime Logistics |
| Container shipping line | 12 Oct 14:10 | China | Transportation & Logistics | Maritime Logistics |
| Shipping network operator | 12 Oct 14:10 | Netherlands | Transportation & Logistics | Maritime Logistics |
| Third-party logistics provider | 12 Oct 14:11 | Hong Kong | Transportation & Logistics | Third-Party Logistics (3PL) |
| Shipbuilder and ship manager | 12 Oct 14:12 | Japan | Manufacturing | Marine & Shipbuilding |
| Port machinery manufacturer | 12 Oct 14:12 | China | Manufacturing | Machinery & Heavy Equipment |
| Dry bulk shipping company | 12 Oct 14:13 | South Korea | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 14:13 | Brazil | Transportation & Logistics | Maritime Logistics |
| Port terminal operator | 12 Oct 14:14 | South Korea | Transportation & Logistics | Maritime Logistics |
| Container shipping line | 12 Oct 14:14 | Singapore | Transportation & Logistics | Maritime Logistics |
| Container terminal operator | 12 Oct 14:15 | Türkiye | Transportation & Logistics | Maritime Logistics |
| Port operator | 12 Oct 14:15 | Brazil | Transportation & Logistics | Maritime Logistics |
| Port agency | 12 Oct 14:16 | Indonesia | Transportation & Logistics | Maritime Logistics |
| Specialty retailer | 13 Oct 10:55 | USA | Consumer Goods & Services | Specialty Retail |
| Confectionery company | 13 Oct 10:56 | USA | Consumer Goods & Services | Food & Beverage |
