Published On : 2026-10-31
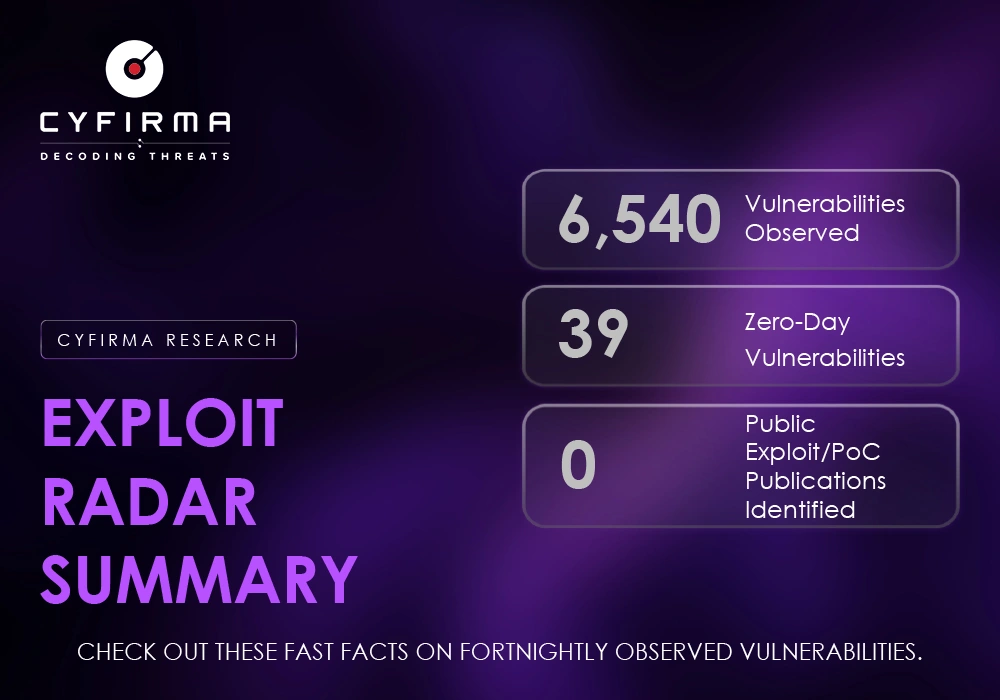
EXPLOIT RADAR SUMMARY
CHECK OUT THESE FAST FACTS ON FORTNIGHTLY OBSERVED VULNERABILITIES.
Most Affected Products/Technologies Observed This Fortnight
Chrome | Linux | MySQL Server
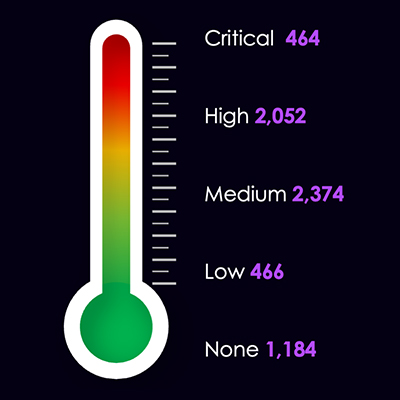
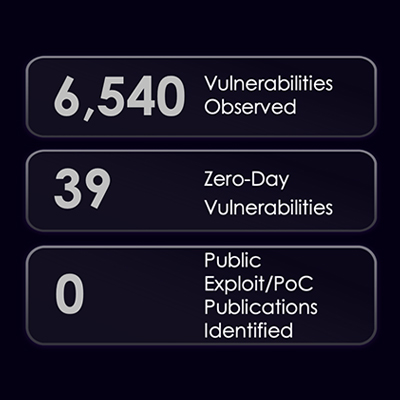
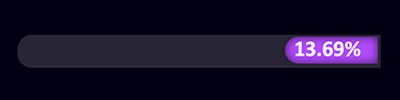
13.69% increase in vulnerabilities compared with the previous two weeks.
Fortnightly Trends in Vulnerabilities
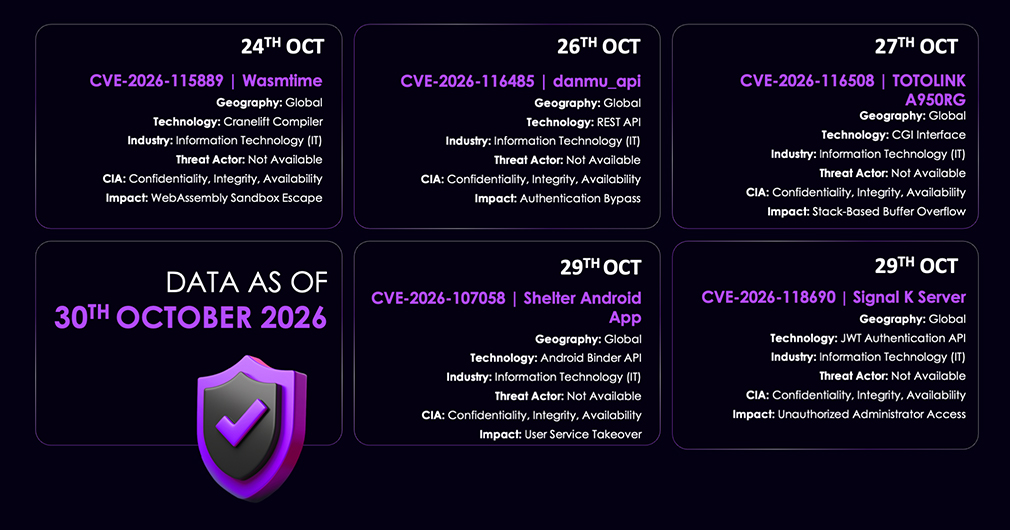
| CVE |
CVSS Score (NVD) |
CVSS 4.0 (NVD) |
Product |
Affected Version |
Fixed Version |
| CVE-2026-115889 |
9.9 |
N/A |
Wasmtime |
< 36.0.19, >= 37.0.0 < 43.0.0 |
36.0.19, 43.0.0 |
| CVE-2026-116485 |
9.8 |
9.3 |
danmu_api |
0 < 1.21.7 |
1.21.7 |
| CVE-2026-116508 |
10 |
9.3 |
TOTOLINK A950RG |
4.1.2cu.5268_B20221104 |
Not specified |
| CVE-2026-107058 |
9.8 |
N/A |
Shelter Android App |
versionCode 445 |
Not specified |
| CVE-2026-118690 |
9.8 |
9.3 |
Signal K Server |
0 < 2.33.0 |
2.33.0 |
Mitigation of CVE
CVE-2026-115889:
- Upgrade Wasmtime to versions 36.0.19 or 43.0.0.
- Avoid compiling untrusted WebAssembly modules using vulnerable versions.
- Restrict access to untrusted Wasm workloads until patched.
- Monitor for unexpected runtime crashes or abnormal execution.
CVE-2026-116485:
- Upgrade danmu_api to 1.21.7 or later.
- Set a strong, unique TOKEN and configure ADMIN_TOKEN.
- Restrict access to environment-management API endpoints.
- Review configuration changes and redeployment activity.
CVE-2026-116508:
- Restrict remote access to the router’s management interface.
- Disable remote administration from the internet.
- Apply firewall rules to block unauthorized requests.
- Contact TOTOLINK for a security update or replace the affected device.
- Monitor for unusual router activity.
CVE-2026-107058:
- Upgrade to a vendor-confirmed patched version when available.
- Avoid using affected Shelter versionCode 445.
- Restrict access to untrusted applications.
- Review Binder service permissions and authentication controls.
- Monitor for unauthorized service or preference modifications.
CVE-2026-118690:
- Upgrade Signal K Server to 2.33.0 or later.
- Restrict access to the /skServer/ziplogs endpoint.
- Rotate the JWT secret key if exposure is suspected.
- Remove unauthorized administrator accounts.
- Review server logs for suspicious access and account creation.
Recommended Customer Prioritization
- CVE-2026-115889 – Wasmtime
Reason: Malicious WebAssembly modules may trigger compiler miscompilation and escape the Wasm sandbox.
- CVE-2026-116485 – danmu_api
Reason: Attackers can bypass authentication and modify server configurations, potentially enabling SSRF and unauthorized redeployment.
- CVE-2026-116508 – TOTOLINK A950RG
Reason: Remote exploitation of the stack-based buffer overflow may compromise affected router devices.
CVE-2026-107058 – Shelter Android App
Reason: Attackers may take over another user’s Binder service API and preference state through unauthorized authentication key registration.
CVE-2026-118690 – Signal K Server
Reason: Unauthenticated attackers can access sensitive log archives, extract JWT secrets, create administrator accounts, and gain full server control.
OVERALL ASSESSMENT
- The identified five CVEs present security risks across application servers, software runtimes, network devices, and Android applications. The vulnerabilities may allow attackers to bypass authentication, gain unauthorized access, modify server configurations, compromise devices, and escape security sandboxes.
Customers should prioritize affected and internet-exposed assets, upgrade to the available fixed versions, strengthen authentication mechanisms, restrict unauthorized access, and monitor suspicious activities. For vulnerabilities without confirmed patches, apply appropriate security controls and follow vendor advisories for updates.
01. DOES THIS AFFECT ME?
- CVE-2026-115889 – Wasmtime: Yes, if you use vulnerable Wasmtime versions with the default Cranelift compiler backend.
- CVE-2026-116485 – danmu_api: Yes, if you use versions below 1.21.7 with the default TOKEN and no ADMIN_TOKEN configured.
- CVE-2026-116508 – TOTOLINK A950RG: Yes, if you use the affected router firmware version 4.1.2cu.5268_B20221104.
- CVE-2026-107058 – Shelter Android App: Yes, if you use the affected Shelter Android app versionCode 445.
- CVE-2026-118690 – Signal K Server: Yes, if you use Signal K Server versions below 2.33.0.
02. HOW EXPOSED AM I?
- Internet-facing vulnerable servers and applications face increased risks of unauthorized access and potential compromise.
- Default or weak authentication configurations may allow attackers to bypass security controls and modify server settings.
- Unpatched network devices may be exposed to remote exploitation, buffer overflow attacks, and device compromise.
- Systems processing untrusted WebAssembly modules may face sandbox escape and potential code execution risks.
- Vulnerable Android applications and outdated software may expose sensitive data, user services, and system configurations to unauthorized access.
03. WHAT SHOULD I DO NOW?
- Upgrade all affected products to their respective fixed versions wherever patches are available.
- Replace default credentials and strengthen authentication and access controls.
- Restrict internet access to vulnerable APIs, servers, and management interfaces.
- Apply firewall rules, network segmentation, and appropriate security controls to protect vulnerable systems.
- Monitor system logs and investigate suspicious activities or unauthorized access.